SSL Certificates Explained – Protecting Your Website & Improving Rankings
Google punishes websites without SSL certificates and an HTTPS connection. Here’s what you need to know to avoid having your website publicly shamed.
Oops! We could not locate your form.
Google punishes websites without SSL certificates and an HTTPS connection. Here’s what you need to know to avoid having your website publicly shamed.
Update – This post was originally written in 2017 and has been updated to reflect changes to browser security indicators, certificate types, and current best practice.
SSL (Secure Sockets Layer) is a standard security technology that protects data being transferred between a website server and a browser. The SSL encrypts data passed between the servers and browsers to ensure that sensitive data remains private and out of the hands of criminals.
It’s worth noting that the term ‘SSL’ is now actually a bit of a misnomer, as it was superseded years ago by TLS (Transport Layer Security), which is what all modern websites actually use. However, ‘SSL’ has stuck as the common shorthand, and you’ll still see it used by certificate providers, hosting companies, and browsers alike. When people refer to an SSL certificate, they mean a TLS certificate. The terms are used interchangeably throughout this post and across the industry.
HTTPS (Hyper Text Transfer Protocol Secure) is a secured version of HTTP, which is a protocol and syntax for transferring data requests and responses online. It is secured by SSL, which encrypts all data being transferred.
HTTPS appears in a website’s URL if a website is secured by a valid SSL certificate. You can confirm this by looking at the address bar in your browser, where a secure site will show https:// at the start of the URL.
The quickest check is to look at your URL in a browser. If it begins with https://, your certificate is in place. If it shows http:// without the S, it isn’t.
It’s worth knowing that browser security indicators have changed significantly in recent years. For a long time, a green padlock icon was the universal signal for a secure site. Google Chrome removed the green colour from the padlock in 2018, then removed the padlock entirely in September 2023, replacing it with a neutral settings icon. Chrome on iOS simply removed the icon altogether. Other major browsers have made similar changes. The reasoning is sound: with HTTPS now the norm rather than the exception, browsers have shifted to only flagging sites that are not secure, rather than highlighting those that are.
So in Chrome today, a secure site simply looks like a normal address bar. An insecure HTTP site will display a clear ‘Not Secure’ warning in the address bar, and that’s what to look out for. Other browsers display similar warnings, though the exact wording varies.

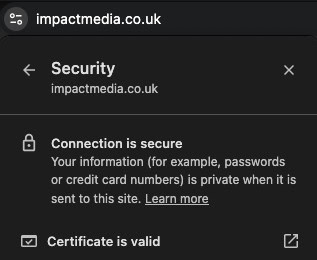
Clicking on the settings icon (or equivalent) in your browser will still reveal the full certificate details if you need to see them.


In past years SSL certificates weren’t required for every business. It was predominately only e-commerce websites and those taking payments that needed one. You’d often see SSL-protected logos on their website at the checkout page, to reassure their users that the website was secure and their payment details safe.
You may be familiar with some of these logos.

However, with online security and data protection becoming more important in recent years, and HTTPS adoption now near-universal, it’s not only websites that process payments that now require SSL certificates. Web users are savvier now and demand that their data be protected and their browsing experience secure. A website flagged as ‘Not Secure’ will prompt many visitors to leave immediately, regardless of whether they were planning to share any sensitive data, and to go a website that shows more regard for their security.
From late October 2017, Google began actively penalising websites without an SSL certificate by warning visitors if they lack one. This is achieved by displaying messages to users in the browser address bar, to warn them if the website they’re about to view is not secure, and has only become more prominent over time.

The bar for what Google considers acceptable has risen, as HTTPS is now considered the baseline, not a bonus. Any site still running on plain HTTP is effectively being publicly flagged as behind the times.
Google considers HTTPS a ranking signal. Websites with a properly implemented SSL certificate and no mixed content issues will likely rank better than those without. This has been Google’s stated position since 2014 and has not changed.
Mixed content, if you’re uncertain, is where a page loads over HTTPS but references images, scripts, or stylesheets via HTTP. This can undermine your certificate’s effectiveness and trigger browser warnings even on an otherwise secured site. It’s worth auditing for this if you’ve recently migrated from HTTP to HTTPS, or haven’t identified and rectified this over the years since you migrated.
This is Google’s way of looking after its customers, setting a precedent that all websites should offer a secure and encrypted connection. It does not look good on them if they are directing users to unsecured sites.
An SSL/TLS certificate provides browsers and users with a website’s security information. Allowing them to view:
1) The name of the certificate holder.
2) A serial number and expiry date.
3) A copy of the certificate holder’s public key.
4) The certificate issuer (the Certificate Authority that has verified it).
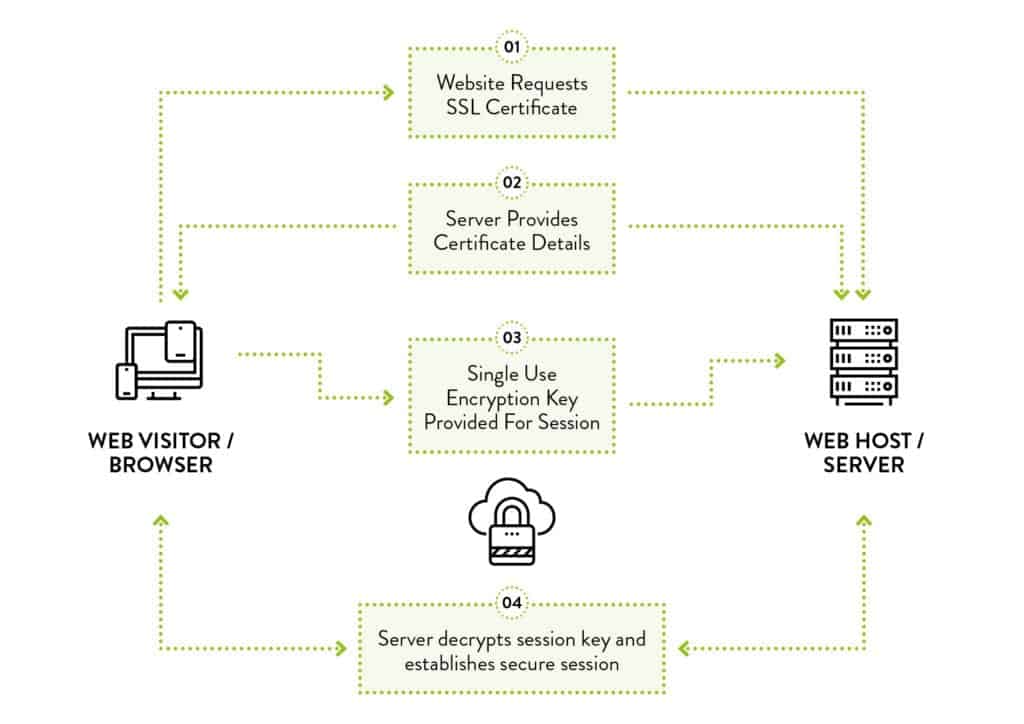
The diagram below shows how the web server and the user’s browser communicate several times before providing a secure connection for the website’s data transfer.

Basically, when a user visits your site, their browser and your server perform a brief exchange, which is called a TLS handshake (very polite and proper) before establishing an encrypted connection. This process verifies the certificate is valid, confirms the server’s identity, and agrees on the encryption method to use. All of this happens in milliseconds before the page loads.
As well as having important SEO repercussions, having SSL protection is a requirement to meet certain standards, and also provides important trust-building. It lets your visitors know that you take security seriously.
In order to accept credit card information on your website, you must pass certain audits that show that you are complying with the Payment Card Industry (PCI) Data Security Standard. Properly implementing TLS/SSL is one of the requirements. Without it, you cannot legally process card payments directly on your site.
Although browsers have moved away from visually rewarding secure sites, the ‘Not Secure’ warning for HTTP sites remains prominent, and it still damages trust. For any visitor considering sharing personal information, card details, or even just a contact form submission, seeing that warning is often enough to make them leave.
A valid SSL certificate removes that friction. It’s a basic expectation of any professional website nowadays.
SSL certificates can be purchased or obtained free of charge. Before going to a third-party provider, it’s worth checking whether your hosting provider already includes one, as most reputable managed hosts now provision SSL certificates automatically.
If you do need to source one independently, a few providers are listed below:
GoDaddy
Digicert
GlobalSign
Comodo
Let’s Encrypt
Thawte
If you’re a technical wizard then you may be able to implement this yourself. If you’re not that comfortable making these kinds of server-level changes then your IT department, your website host or your website agency will be able to do this for you.
SSL implementation is included as standard in our WordPress Support & Maintenance plans.
As with everything, there are both free and paid options.
Let’s Encrypt is a free, automated, non-profit Certificate Authority that has issued certificates for hundreds of millions of domains worldwide. Despite being free, it provides the level of encryption needed to protect the vast majority of websites. Let’s Encrypt certificates are valid for 90 days and are designed to be renewed automatically.
Let’s Encrypt also supports wildcard certificates, a feature it has offered since March 2018. This means it can secure all subdomains of a domain under a single certificate, free of charge (more on wildcards below).
As noted above, many managed hosting providers now include Let’s Encrypt certificates and provision them automatically, so there may be nothing to do on your end at all.
If you are taking payments online or have a membership/subscription website that stores personal data, a paid SSL might serve you better.
Paid certificates offer Organisation Validation (OV) and Extended Validation (EV) options, which go beyond simply verifying domain ownership:
A paid SSL is charged and renewed yearly, and you should be looking to pay between £100-500. Depending on the provider and level of the certificate (i.e. Wildcard). Some may appear cheaper, however, please check the renewal fees. As some companies run discounts on the first year and then hike the price at the renewal stage.
A standard SSL certificate covers a single domain (e.g. www.impactmedia.co.uk). A wildcard certificate covers all subdomains of a domain under a single certificate (e.g. blog.impactmedia.co.uk, shop.impactmedia.co.uk, and so on), which is useful if you run multiple subdomains or a WordPress Multisite network.
As noted above, Let’s Encrypt now offers wildcard certificates for free, via DNS challenge validation. Paid wildcard certificates are also available from commercial providers if you require OV or EV validation.
To achieve the same effect as a wildcard certificate with most other free options, you’d need to implement an individual certificate for each variant mentioned above. Quite a bit of legwork.
Although the SSL/TLS will encrypt data whilst in transit, it won’t protect your website from being hacked. A certificate tells your visitors their connection is encrypted, it says nothing about whether the site itself is secure. Adding additional security, like a Web Application Firewall (WAF), keeping plugins and themes updated, and using a managed hosting environment with proactive monitoring are the layers that protect the site itself.
If you’re looking for additional protection alongside SSL, and ongoing support and maintenance for your WordPress or WooCommerce website, our WordPress Support & Maintenance plans cover all of this as standard.
You can request our Support Brochure to see our current plans, inclusive features and pricing.

If you’d like to learn more about our WordPress & WooCommerce Support & Maintenance plans, drop us an email or give James a call.
Our plans provide a holistic solution to your website’s performance, reliability and security, and are inclusive of premium tools and services.